For automotive and embedded software teams, compliance often becomes a major challenge toward the end of a project.
The development work may be progressing well. Requirements have been created, software has been implemented, tests have been executed, and reviews have taken place. Then the team starts preparing for an assessment or customer review and discovers that some requirements are not linked to tests, approvals are sitting in emails, change decisions are difficult to trace, or important evidence is spread across multiple tools.
That is when a simple question becomes difficult to answer:
Can we prove how this requirement moved from definition to implementation and verification?
A compliance-ready software lifecycle addresses this problem by making compliance part of everyday engineering rather than treating it as an activity that happens just before an assessment.
For automotive organizations working with Automotive SPICE, ISO 26262, or other process and safety expectations, this approach can help create a more structured connection between requirements, development, testing, reviews, changes, and evidence.
If you are starting with the fundamentals, understanding what functional safety means in software development provides useful context for why these activities matter throughout the product lifecycle.
What Is a Compliance-Ready Software Lifecycle?
A compliance-ready software lifecycle is a development process where the activities needed to demonstrate compliance are built into the normal engineering workflow.
It does not mean creating a separate compliance process that runs alongside development.
Instead, the objective is to make activities such as:
- Requirements review
- Traceability
- Design verification
- Software testing
- Change management
- Safety reviews
- Approvals
- Configuration management
- Evidence collection
part of the lifecycle itself.
The V-model provides a useful way to understand this approach.
On the left side, teams progressively define what the system needs to do. Requirements are refined from stakeholder needs into system and software requirements, followed by architecture and detailed design.
On the right side, those engineering decisions are progressively verified through implementation, integration, testing, verification, and validation.
A compliance-ready lifecycle connects both sides.
For example:
Requirement → Architecture → Implementation → Test → Result → Evidence
If those relationships are maintained throughout development, the organization does not need to reconstruct them later.
This is particularly important when considering the relationship between Automotive SPICE and ISO 26262. ASPICE vs ISO 26262: Understanding the Differences explains how process improvement and functional safety address different but complementary aspects of automotive development.
Embedding Compliance Checkpoints Into the V-Model
One of the biggest differences between a reactive and proactive compliance approach is when compliance is considered.
A reactive approach might look like this:
Develop → Test → Prepare for Assessment → Find Gaps → Fix Evidence
A compliance-ready approach looks more like:
Plan → Develop → Review → Verify → Capture Evidence → Continue
The difference may seem small, but it can have a significant effect on the project.
Compliance Should Not Be a Final Gate
Imagine a project that has been running for 12 months.
Thousands of requirements have been created. Hundreds of tests have been executed. Multiple software versions have been released internally.
Three weeks before an assessment, the team starts checking traceability.
They discover:
- Several requirements have no verification link.
- Some requirements changed without a documented impact assessment.
- Test evidence exists, but it is stored separately.
- A few reviews were completed through email.
- Some older documents do not match the current baseline.
Now the team has to reconstruct months of engineering activity.
This is exactly what compliance checkpoints are designed to prevent.
Instead of waiting until the end, checkpoints can be introduced at important V-model stages.
Example of V-Model Compliance Checkpoints
Lifecycle Stage | Example Checkpoint |
Stakeholder Requirements | Review completeness and sources |
System Requirements | Approval and traceability |
Software Requirements | Quality, consistency, testability |
Architecture | Requirement-to-architecture relationships |
Detailed Design | Design review and coverage |
Implementation | Coding and review evidence |
Unit Verification | Test coverage and results |
Integration | Integration evidence and defect resolution |
System Verification | Requirement verification |
Validation | Validation evidence and approvals |
Release | Baseline, open issues and evidence review |
These checkpoints do not have to become large meetings.
In many cases, a checkpoint can be a defined workflow state, review, approval, or automated report.
The important thing is that the team knows what must be completed before moving to the next stage.
If those relationships are maintained throughout development, the organization does not need to reconstruct them later. Organizations looking to establish these connected workflows can explore ALM consulting services to support requirements, testing, traceability, and compliance activities across the lifecycle.
Make the Checkpoint Part of the Workflow
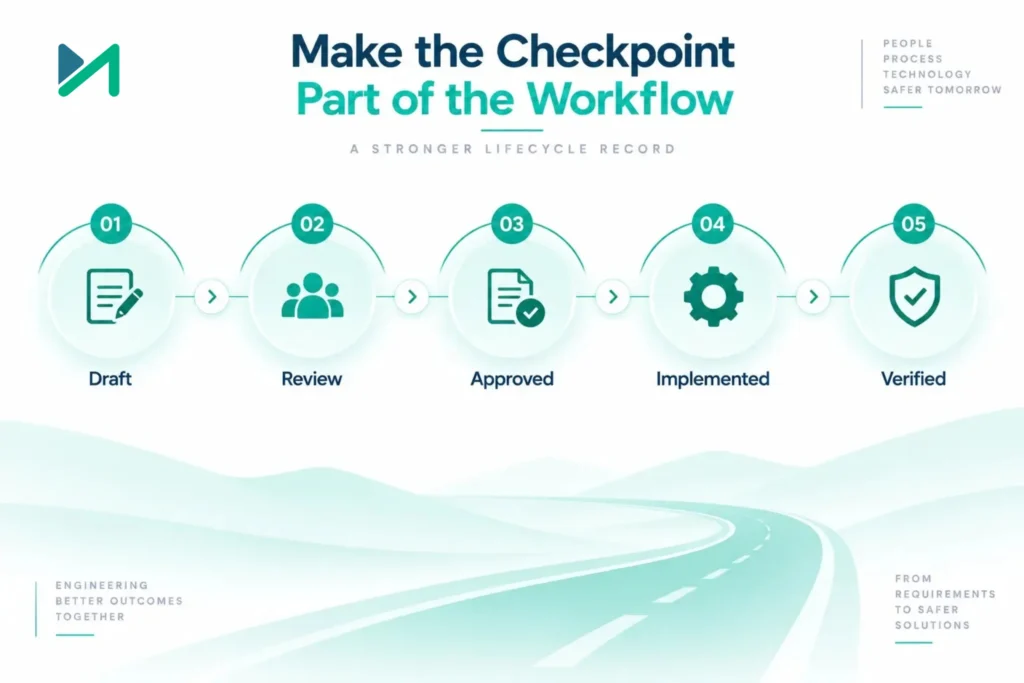
Consider a software requirement.
Instead of simply marking it “Complete”, the workflow could require:
Draft → Review → Approved → Implemented → Verified
Each stage provides useful information.
The requirement has been reviewed.
Someone has approved it.
Implementation has been completed.
Verification has been performed.
The result is a much stronger lifecycle record than a document that simply says the requirement exists.
The goal is not more checkpoints. The goal is meaningful checkpoints at the right points in the development lifecycle.
Build a Documentation and Evidence Strategy
Documentation is one of the areas where compliance efforts can become unnecessarily complicated.
Teams sometimes assume that being compliant means producing more documents.
That is not necessarily the objective.
The more useful question is:
What evidence would demonstrate that the required engineering activity actually happened?
That changes how teams think about documentation.
Start With the Evidence You Need
For requirements management, evidence might include:
- Requirement definition
- Requirement source
- Review history
- Approval
- Traceability
- Change history
- Verification relationship
For testing, evidence could include:
- Test case
- Test environment
- Test execution
- Test result
- Defect information
- Retest result
- Requirement coverage
For change management, evidence could include:
- Change request
- Reason for change
- Impact analysis
- Approval
- Updated engineering artefacts
- Verification results
This creates an evidence chain.
Requirement → Change → Impact Analysis → Implementation → Verification → Approval
That chain becomes particularly valuable when someone asks a question months after the original decision.
A compliance-ready process therefore treats evidence as a by-product of engineering activity, rather than something that needs to be recreated later. For organizations managing complex requirements, verification, changes, and evidence, IBM ELM consulting services can help provide a structured environment for connecting these engineering activities.
Evidence Should Be Created During Engineering
Consider a safety-related requirement that changes after testing has already started.
If the project has good traceability, the team can identify the related engineering artefacts and determine what needs to be reviewed.
If the project does not, someone may need to manually search through documents, spreadsheets, test reports, and emails.
The second approach creates unnecessary risk.
A compliance-ready process therefore treats evidence as a by-product of engineering activity, rather than something that needs to be recreated later.
This is also where functional safety compliance tools can become useful. The right tools can help teams manage relationships between requirements, safety activities, verification, changes, and supporting evidence.
But there is an important distinction:
A tool can help manage evidence. It cannot replace a well-defined engineering process.
Traceability Should Connect the Lifecycle
Traceability is often discussed in the context of compliance, but its value goes beyond an assessment.
Good traceability helps engineering teams understand how one decision affects another.
For example:
A stakeholder need leads to a system requirement.
That system requirement is refined into software requirements.
Those requirements influence architecture and design.
The design is implemented.
Tests are created to verify the implementation.
Test results demonstrate whether the requirements were satisfied.
Now imagine that the original requirement changes.
The team needs to understand what else might be affected.
That is where traceability becomes practical engineering infrastructure.
Forward and Backward Traceability
A compliance-ready lifecycle should support both directions.
Forward traceability:
Requirement → Design → Implementation → Test
This helps answer:
“How was this requirement implemented and verified?”
Backward traceability:
Test → Requirement → Source
This helps answer:
“Why does this test exist, and what requirement does it verify?”
Both perspectives are useful.
Without them, teams may have plenty of individual artefacts but still struggle to explain how those artefacts relate to each other.
Define Roles and Responsibilities Early
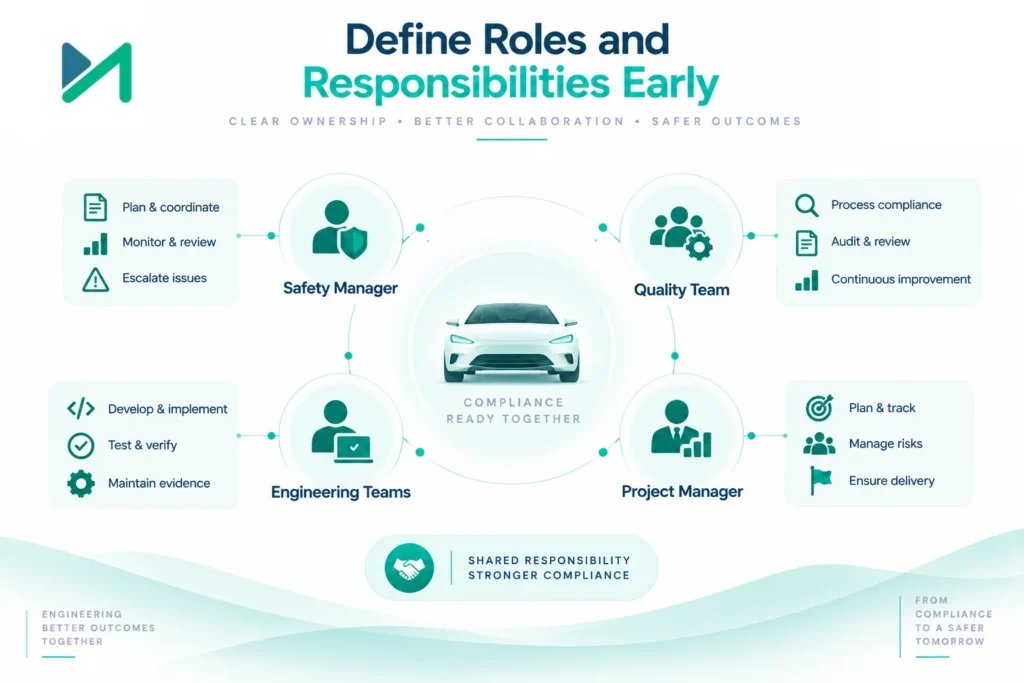
Compliance becomes difficult when responsibility is unclear.
A common situation is that everyone is involved in compliance, but nobody knows exactly who owns which activity.
Engineering assumes Quality handles it.
Quality assumes Safety owns it.
Safety expects Engineering to maintain the evidence.
The result is often gaps and duplicated effort.
A compliance-ready lifecycle should define responsibilities before development gets too far.
The Safety Manager
The safety manager or functional safety role helps coordinate safety-related activities across the lifecycle.
Depending on the organization and project, responsibilities may include:
- Coordinating the safety plan
- Monitoring safety-related activities
- Supporting safety analyses
- Coordinating safety reviews
- Tracking safety work products
- Supporting confirmation activities
- Escalating unresolved safety issues
The important point is that the safety role should be involved early rather than appearing near the end of the project to collect evidence.
Functional safety needs to influence engineering decisions while those decisions are still being made.
The Quality Team
Quality has a different but equally important role.
Quality teams may be responsible for:
- Process audits
- Process compliance
- Work-product quality
- Assessment preparation
- Corrective actions
- Process improvement
- Objective evidence
However, Quality should not become the department responsible for creating every piece of project evidence.
The engineering team should generate evidence through its normal activities.
Quality provides oversight and helps determine whether the defined process is being followed effectively.
Engineering Teams
Developers, architects, requirements engineers, testers, and project managers also have direct responsibilities.
For example:
Requirements engineers maintain clear, consistent, and traceable requirements.
Architects maintain appropriate relationships between requirements and architecture.
Developers follow development, review, and change-control practices.
Test engineers create and maintain verification evidence.
Project managers monitor lifecycle activities, dependencies, risks, and milestones.
Safety and Quality teams provide oversight, guidance, review, and escalation.
This creates a healthier model:
Compliance is not owned by one department. It is supported by clearly defined responsibilities across the lifecycle.
Continuous Compliance vs. the End-of-Project Scramble
There is a familiar pattern in many engineering organizations.
The assessment date gets closer.
Someone asks for the latest traceability report.
Another person starts checking requirements.
A missing test is discovered.
Someone searches an email thread for an approval.
A change was implemented three months ago, but the impact analysis cannot be found.
Now engineers have to stop their current work and reconstruct the project history.
This is the end-of-project scramble.
The Reactive Model
It often looks like:
Develop → Test → Collect Documents → Identify Gaps → Rework → Assessment
The problem is that the gaps are discovered too late.
The Continuous Model
A more sustainable lifecycle looks like:
Plan → Develop → Review → Capture Evidence → Monitor → Improve
Evidence is maintained as part of normal engineering.
When a requirement is approved, the approval is recorded.
When a design changes, the change is controlled.
When a test is executed, the result is retained.
When a defect is identified, it is connected to the appropriate engineering activity.
When a safety-related requirement changes, the impact can be assessed before the change is released.
The organization does not necessarily perform less work.
Instead, the work is distributed throughout the lifecycle instead of being concentrated into a stressful period before an assessment.
Create a Continuous Compliance Workflow
A practical compliance-ready workflow can be structured around eight steps.
1. Define
Establish requirements, applicable standards, safety objectives, lifecycle activities, and responsibilities.
2. Plan
Define reviews, verification activities, evidence expectations, and project milestones.
3. Develop
Perform requirements engineering, architecture, implementation, integration, and testing according to the defined process.
4. Connect
Maintain relationships between requirements, design, implementation, tests, defects, changes, and approvals.
5. Review
Perform engineering, safety, and quality reviews at appropriate lifecycle points.
6. Verify
Confirm that requirements have appropriate verification and that the resulting evidence is available.
7. Baseline
Place approved artefacts under appropriate configuration and change control.
8. Monitor
Continuously identify incomplete evidence, process gaps, deviations, and risks.
This workflow changes the question from:
Are we ready for the assessment?
to:
Are we following the defined process today?
That is a much healthier way to approach compliance.
Where ALM Fits Into a Compliance-Ready Lifecycle
At a small project scale, spreadsheets and separate documents may appear manageable.
As the number of requirements, engineers, variants, tests, releases, and changes increases, maintaining all the relationships manually becomes much harder.
This is where an ALM platform can support the process.
A structured ALM environment can help connect activities such as:
- Requirements management
- Traceability
- Reviews and approvals
- Development
- Test management
- Defect management
- Change management
- Configuration management
- Reporting
The value is not simply having all information in one place.
The bigger benefit is being able to understand the relationships between engineering activities.
For example, when a requirement changes, the team should be able to identify related artefacts and determine what needs to be reviewed or retested.
When an assessor asks how a requirement was verified, the team should be able to follow the relationship to the relevant test and evidence.
When a project manager wants to understand lifecycle status, the information should come from the engineering process rather than from manually prepared spreadsheets.
If your organization is dealing with disconnected requirements, testing, changes, and compliance evidence, MicroGenesis ALM Services can help you explore how a structured ALM approach can support the wider engineering lifecycle.
Tools Should Support the Process, Not Become the Process
It is tempting to think that implementing an ALM platform automatically makes a project compliance-ready.
It does not.
A tool cannot decide:
- Which activities are mandatory
- Who should approve a requirement
- What evidence is appropriate
- Which safety activities apply
- How the organization should manage exceptions
- What constitutes an acceptable engineering process
Those decisions belong to the organization and its engineering governance.
The tool should then make the agreed process easier to execute.
This distinction is important because a poorly designed workflow can simply move administrative complexity from spreadsheets into an ALM system.
The objective should be different.
The tool should make the right engineering behavior easier.
For example, if a requirement cannot move to an approved state until the required review is completed, the workflow itself helps enforce the process.
If a change cannot be completed without an impact assessment, the system can make that activity visible.
If a test result is connected directly to a requirement, evidence becomes easier to follow.
That is where technology adds practical value.
How MicroGenesis Supports Connected Engineering Processes
Building a compliance-ready lifecycle is not simply about selecting a tool.
The more important question is how requirements, development, testing, change management, and compliance activities should work together within the organization’s existing engineering process.
Consider a common situation.
A safety-related software requirement changes after implementation has already started.
The team needs to understand what is affected, assess the impact, review the change, update the relevant engineering artefacts, perform the required verification, and retain the evidence.
If those activities are disconnected, the process can quickly become manual.
If they are connected, the team has a clearer path from change to impact to verification.
That is the kind of lifecycle connection organizations should aim for.
MicroGenesis works with organizations around ALM processes, including requirements management, traceability, development workflows, testing, change management, and compliance-oriented engineering practices.
If your team is spending significant time before every assessment trying to reconstruct requirements, approvals, test results, and change history, it may be worth looking at the lifecycle as a whole rather than fixing each documentation gap separately.
You can explore MicroGenesis ALM Software Solutions to understand how an ALM-led approach can support connected engineering processes.
Building Compliance Into the Engineering Culture
A compliance-ready lifecycle ultimately depends on more than standards, templates, and tools.
It depends on how people work.
Engineers need to understand why traceability matters.
Project managers need visibility into process gaps before they become project risks.
Safety teams need to participate early.
Quality teams need to monitor process effectiveness rather than simply collect documents.
And engineering teams need a practical way to maintain evidence without turning every activity into an administrative exercise.
This is especially important for organizations working with both Automotive SPICE and ISO 26262.
The two frameworks address different aspects of engineering discipline and safety, but they can intersect heavily in areas such as requirements management, verification, traceability, change management, and evidence.
A well-designed lifecycle therefore does not treat them as two completely separate compliance exercises.
Instead, the organization can establish a common engineering foundation and incorporate the specific activities and evidence required by each applicable framework.
Final Thoughts
A compliance-ready software lifecycle is not created by producing a large documentation package just before an assessment.
It is created by embedding the right activities into everyday engineering.
That means putting meaningful compliance checkpoints into the V-model.
It means defining what evidence needs to be produced and capturing it while the work is happening.
It means clearly assigning responsibilities across Safety, Quality, Engineering, and Project Management.
And perhaps most importantly, it means replacing the end-of-project compliance scramble with continuous visibility.
The objective is straightforward:
Know what was required.
Know what was developed.
Know what changed.
Know what was tested.
Know who reviewed it.
And be able to demonstrate the connection.
When compliance becomes part of the software lifecycle rather than a separate activity at the end, engineering teams can spend less time reconstructing the past and more time improving the product they are building.