As software takes on more responsibility in modern vehicles, functional safety in software development has become a core engineering concern. Software now influences functions such as braking, steering, power management, battery systems, and driver assistance.
This raises a practical question for software teams: What happens when the software does not behave as expected?
Functional safety focuses on reducing the risk that malfunctions in electrical and electronic systems could lead to hazardous situations. It is not only about making software work correctly under normal conditions. It is also about identifying potential failures, detecting them, and defining how the system should respond.
For automotive development, ISO 26262 provides a structured framework for managing functional safety throughout the product lifecycle.
In this guide, we will explain functional safety, the scope of ISO 26262, ASIL classification, the safety lifecycle from concept to production, and why software teams need a safety mindset.
What Is Functional Safety?
Functional safety focuses on preventing unreasonable risk caused by the malfunctioning behavior of electrical and electronic systems.
Consider an electronic control system that monitors vehicle speed. Under normal conditions, it receives information from sensors and uses that information to support a vehicle function.
Now imagine the sensor starts sending incorrect data.
A functional safety approach asks:
- Can the system detect the incorrect information?
- What happens if the incorrect value is used?
- Can the software recognize the fault?
- Should the system move to another operating mode?
- Should a warning be generated?
- How will the expected behavior be verified?
The objective is not simply to eliminate every possible failure. Functional safety provides a systematic approach for identifying risks and defining appropriate responses.
This becomes increasingly important as automotive software becomes connected to functions that can affect physical vehicle behavior.
What Is ISO 26262?
ISO 26262 is an international standard for the functional safety of electrical and electronic systems in road vehicles.
It provides a framework for managing safety throughout the lifecycle, beginning with the concept phase and continuing through development, production, operation, service, and decommissioning.
For software teams, ISO 26262 can influence:
- Software requirements
- Software architecture
- Software design
- Implementation
- Unit verification
- Software integration
- Testing
- Configuration management
- Change management
- Safety documentation
- Verification and validation
Functional safety is therefore not simply a final testing activity.
If safety is considered only when software is ready for testing, teams may discover that requirements or architecture decisions need to be changed. Addressing safety earlier makes it easier to build the necessary controls into development.
ASPICE and ISO 26262 Are Not the Same
Automotive teams often work with both ASPICE and ISO 26262, but they address different aspects of development. ASPICE focuses on development process assessment and improvement, while ISO 26262 provides a framework for functional safety.
If your team is working with both frameworks, our guide on ASPICE vs ISO 26262 explains their differences and where they intersect.
What Does ISO 26262 Cover?
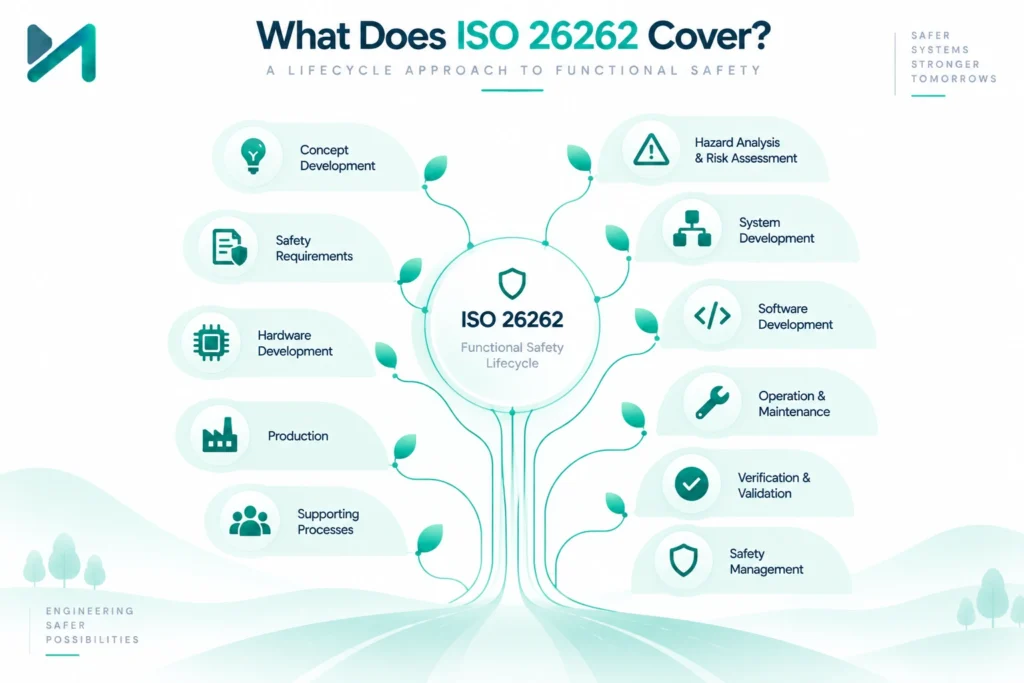
ISO 26262 takes a lifecycle-based approach to functional safety.
Its activities span areas such as:
- Concept development
- Hazard analysis and risk assessment
- Safety requirements
- System development
- Hardware development
- Software development
- Production
- Operation and maintenance
- Supporting processes
- Safety management
- Verification and validation
For software organizations, this means safety requirements need to connect with the broader engineering process.
A safety requirement should not simply exist in a document. Teams need to understand:
Where did the requirement come from?
Which software component implements it?
How will it be verified?
What happens if the requirement changes?
That is where requirements management and traceability become important.
Why Functional Safety Matters in Software Development
Software in an automotive system rarely operates on its own. It may receive information from sensors, communicate with other ECUs, process data, make decisions, and control physical functions.
Consider a simplified braking-related example.
A functional requirement might state:
The software shall calculate the requested braking value based on valid input conditions.
A functional safety perspective asks additional questions:
- What if the input is invalid?
- What if the sensor stops responding?
- What if the calculated value is outside the expected range?
- How quickly should the fault be detected?
- What should the system do after detecting it?
- How will the behavior be tested?
This changes the conversation from:
“Does the feature work?”
to:
“Does the feature behave as expected, including when something goes wrong?”
ASIL Classification Basics
One of the most important concepts in ISO 26262 is the Automotive Safety Integrity Level, or ASIL.
ASIL is used to classify safety requirements according to the risk associated with a hazardous event.
The levels are:
- ASIL A
- ASIL B
- ASIL C
- ASIL D
ASIL D represents the highest level within the ASIL scale. There is also QM, or Quality Management, for situations where the safety analysis does not require an ASIL classification.
ASIL should not be treated simply as a label added to a requirement. It can influence the rigor expected during development and verification.
How Is ASIL Determined?
ASIL determination considers three main factors:
Severity
How serious could the consequences be if the hazardous event occurs?
Exposure
How frequently could the relevant operational situation occur?
Controllability
How difficult would it be for the driver or another person to control or avoid the hazardous situation?
These factors are considered during safety analysis to determine the appropriate classification.
What Does ASIL Mean for Software Teams?
ASIL can influence practical engineering activities such as:
- Requirements development
- Software architecture
- Software decomposition
- Error handling
- Fault detection
- Verification
- Testing
- Change management
- Configuration management
- Documentation
- Traceability
Imagine a software component handling a safety-related function. A change that looks small from a coding perspective could potentially affect its safety behavior.
Before making the change, the team should be able to determine:
- Which safety requirements are associated with the component?
- What other components depend on it?
- Which tests verify the behavior?
- Does the change affect safety-related assumptions?
- Is additional verification required?
A practical question for your software team: If a developer changes a safety-related component today, can you quickly identify the affected requirements, related tests, and approval history?
If not, the challenge may be how engineering information is connected rather than the team’s technical capability.
The Functional Safety Lifecycle: From Concept to Production
Functional safety begins before software development and continues beyond software release.
A simplified lifecycle is:
Concept → Hazard Analysis → Safety Goals → Requirements → Architecture → Implementation → Verification → Validation → Production
1. Concept Phase
The team defines the intended function, operating conditions, system boundaries, and potential hazards.
The key question is:
What could go wrong, and what must the system do to control the resulting risk?
2. Hazard Analysis and Risk Assessment
Potentially hazardous situations are identified and evaluated. Severity, exposure, and controllability contribute to safety goals and ASIL classification.
3. Define Safety Requirements
Safety goals are translated into detailed requirements.
For example:
Safety Goal: Prevent unintended activation of a critical vehicle function.
This may lead to requirements for input monitoring, fault detection, diagnostics, safe-state transitions, and fault communication.
4. Design the Safety Architecture
The engineering team determines how the system will achieve the required safety behavior. Depending on the system, this may include monitoring, diagnostics, redundancy, fault detection, and safe-state mechanisms.
5. Software Development
Developers implement the allocated software requirements while paying attention to interfaces, error handling, coding practices, configuration, and change control.
Developers should understand why a requirement exists, not simply its ASIL classification.
6. Verification and Validation
Activities can include:
- Requirements reviews
- Design reviews
- Static analysis
- Unit testing
- Integration testing
- Simulation
- Fault-injection testing
- Hardware-in-the-loop testing
- System testing
Every safety-related requirement should have a defined way to demonstrate that it has been satisfied.
7. Production and Release
Before release, organizations need confidence that approved requirements were implemented, safety-related changes were controlled, verification was completed, traceability is maintained, and the released configuration is known.
If your team is collecting safety evidence manually at the end of a project, the process may need to be connected earlier. Requirements, development, testing, and compliance evidence should be maintained throughout the lifecycle.
For organizations looking to establish a structured engineering lifecycle, MicroGenesis ALM Solutions can support requirements management, traceability, workflows, testing, and lifecycle process improvement.
Why Software Teams Need a Safety Mindset
Functional safety should not belong only to the safety or quality team.
Systems engineers, architects, developers, testers, hardware engineers, and project managers can all influence the final safety outcome.
Consider a developer changing an error-handling routine while fixing an unrelated issue. If that routine supports a safety-related function, the change could affect safety behavior.
A safety mindset encourages questions such as:
- Does this change affect a safety requirement?
- What happens when an input is invalid?
- What happens if communication fails?
- Does the change affect a safe-state mechanism?
- Which tests verify the behavior?
The goal is not to make every developer a safety engineer. The goal is to make safety part of everyday engineering decisions.
Functional Safety and Requirements Traceability
Traceability connects safety goals with the engineering work needed to implement and verify them.
A simplified chain is:
Safety Goal → System Safety Requirement → Software Safety Requirement → Architecture → Implementation → Test Case → Test Result
This allows teams to answer practical questions:
- Where did the requirement come from?
- Where is it implemented?
- Which test verifies it?
- What happens if it changes?
If answering these questions requires searching through spreadsheets, documents, emails, and separate testing systems, the development process may lack sufficient integration.
A structured ALM process can help connect requirements, development, testing, changes, and compliance evidence.
Functional Safety vs Software Quality
Functional safety and software quality are related, but they are not identical.
Software quality asks:
Does the software perform its intended function correctly?
Functional safety also asks:
What happens if the software or related system malfunctions, and are appropriate measures in place to control the resulting risk?
Software may pass normal functional tests while still requiring additional consideration for situations such as:
- Invalid sensor data
- Communication failures
- Unexpected inputs
- Component failures
- Unexpected calculations
This is why functional safety should complement software quality rather than replace it.
Common Functional Safety Challenges
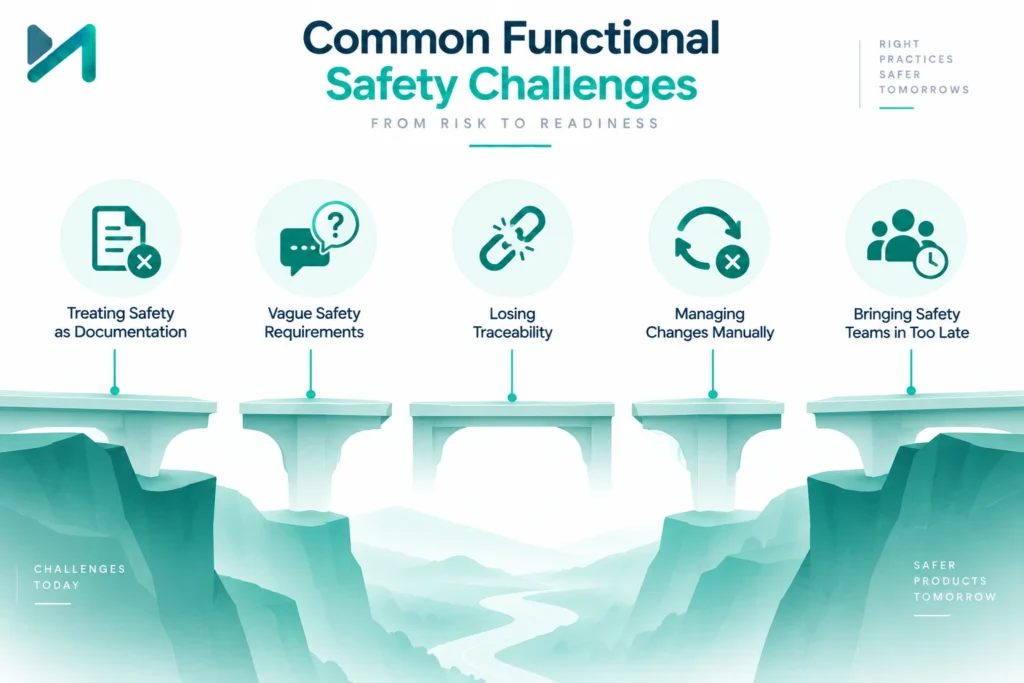
Treating Safety as Documentation
Documentation is important, but it should reflect actual engineering activities. Safety needs to influence requirements, design, development, testing, and change management.
Writing Vague Safety Requirements
A statement such as:
The system shall respond safely to faults.
does not explain what “safely” means, when the response should occur, or how it should be tested.
Requirements need enough detail to be understood, implemented, and verified.
Losing Traceability
When requirements, tests, implementation, and compliance evidence are stored separately, maintaining relationships becomes difficult.
Managing Changes Manually
A requirement change may affect architecture, software, hardware, tests, safety analysis, and documentation. Manual impact analysis can easily miss relationships.
Bringing Safety Teams in Too Late
If safety considerations are introduced near the end of development, changes to requirements or architecture can become more difficult and expensive.
What Should Functional Safety and Compliance Tools Provide?
As projects grow, maintaining requirements, traceability, testing, changes, and compliance evidence manually becomes increasingly difficult.
A functional safety or lifecycle management environment should help connect:
- Safety goals
- Requirements
- Architecture
- Software
- Hardware
- Tests
- Defects
- Changes
- Baselines
- Compliance evidence
If you’re evaluating tools, our guide on Functional Safety and Compliance Tools explains the key capabilities to consider.
Useful capabilities include:
- Requirements management
- Traceability
- Baseline management
- Change management
- Impact analysis
- Test management
- Compliance reporting
Don’t start with the tool feature list alone. Start with your engineering process. Ask where requirements are created, who approves them, how changes are handled, where test evidence lives, and how traceability will be demonstrated.
Building a Compliance-Ready Software Development Process
Functional safety should be built into development rather than treated as an activity performed just before an assessment.
A compliance-ready process connects:
Requirements → Design → Implementation → Verification → Evidence
When requirements change, the process should support:
Change Request → Impact Analysis → Approval → Implementation → Verification → Updated Evidence
Teams should be able to maintain approved requirements, control changes, preserve traceability, connect requirements with verification, and maintain evidence throughout development.
If your team is preparing compliance evidence manually at the end of every release, it may be time to move that evidence closer to the engineering work itself.
Our guide on building a compliance-ready software development process explains how engineering teams can structure this approach.
Ask yourself one simple question: If an assessor requested the complete history of one safety requirement, could your team show its source, approvals, implementation, verification, and changes without rebuilding the trail manually?
How to Build a Functional Safety Mindset
A practical safety mindset can be built without making development unnecessarily complicated.
Explain the Safety Intent
Developers should understand why a safety requirement exists, not simply its ASIL level.
Make Safety Requirements Visible
Teams should be able to identify safety-related requirements and their relationships with other engineering artifacts.
Connect Development and Testing
Developers should understand how safety-related functionality will be verified.
Review Changes for Safety Impact
A change should be assessed for its potential effect on requirements, interfaces, assumptions, and verification.
Automate Where Practical
Automated traceability, reporting, testing, and quality checks can reduce repetitive manual work.
Maintain Evidence Throughout Development
Do not wait until the end of the project to recreate the evidence needed for compliance.
The simplest way to build a safety mindset is to make safety questions part of existing engineering conversations.
How MicroGenesis Can Support Functional Safety and ALM
Functional safety becomes difficult to manage when requirements, development activities, testing, and compliance evidence are spread across different tools and teams.
The real challenge is not simply having a requirements tool. It is being able to follow the complete story of a safety requirement, from where it originated to how it was implemented and how the team verified it.
For example, when a safety requirement changes, an engineering team should be able to identify what else might be affected, review the change, update the relevant implementation and tests, and retain the evidence of what was done.
That is where an integrated ALM approach can help.
MicroGenesis works with organizations to improve how engineering teams manage requirements, traceability, development workflows, testing, changes, and compliance activities across the product lifecycle.
If your team is spending significant time manually connecting requirements with tests, changes, and compliance evidence, it may be worth looking at the process as a whole rather than solving each issue separately.
You can explore MicroGenesis ALM Services to learn more about establishing a structured lifecycle approach.
For organizations working with IBM’s engineering ecosystem, IBM Engineering Lifecycle Management can provide a connected environment for managing requirements and other engineering lifecycle activities.
Conclusion
Functional safety in software development is about preparing systems to behave appropriately when something goes wrong.
For automotive organizations, ISO 26262 provides a structured framework for managing functional safety from concept through production.
For software teams, the practical principles are straightforward:
- Understand the safety purpose behind requirements.
- Identify the appropriate ASIL classification.
- Consider safety from the beginning.
- Write clear and verifiable safety requirements.
- Maintain traceability between requirements, implementation, and tests.
- Evaluate changes for safety impact.
- Keep safety evidence connected to engineering activities.
- Make functional safety part of everyday software development.
The strongest safety processes are not created by adding documentation at the end of a project. They are built by making safety part of how teams define requirements, design systems, develop software, test changes, and maintain traceability throughout the lifecycle.