Automotive software development is no longer just about writing code, testing features, and delivering a release. Modern vehicles depend on interconnected software systems that influence braking, steering, driver assistance, connectivity, diagnostics, and cybersecurity. As software complexity increases, automotive companies must demonstrate that their development processes are controlled, their safety risks are addressed, and their products are protected against cybersecurity threats.
This is where automotive software compliance becomes important.
For OEMs and suppliers, three frameworks frequently shape engineering expectations: Automotive SPICE (ASPICE), ISO 26262 for functional safety, and ISO/SAE 21434 for automotive cybersecurity. Although they address different concerns, they influence many of the same engineering activities, including requirements management, architecture, development, testing, change control, and verification.
The challenge is not simply understanding each standard. It is understanding how they work together and how to maintain evidence throughout the software lifecycle.
What Is Automotive Software Compliance?
Automotive software compliance refers to the processes, engineering practices, and evidence used to demonstrate that automotive software development meets applicable process, safety, cybersecurity, and customer requirements.
Compliance expectations depend on the product, its intended use, the applicable standards, contractual obligations, and the OEM’s supplier requirements.
For example, a supplier developing software for a vehicle braking controller may need to demonstrate how safety requirements are derived, implemented, verified, and linked to relevant safety analyses. A supplier developing a connected infotainment system may face different safety considerations but still need to address cybersecurity, software quality, and integration requirements.
In both cases, compliance must be supported by engineering evidence, not just policy documents.
Understanding compliance-ready software development is a useful starting point for building these practices into everyday development activities.
Automotive SPICE: Assessing Engineering Process Capability
Automotive SPICE, commonly called ASPICE, is a process assessment model used in the automotive industry to evaluate the capability of development processes.
It helps organizations assess whether engineering activities are performed systematically, managed effectively, and supported by appropriate work products and evidence.
ASPICE commonly influences areas such as:
- System and software requirements analysis
- System and software architecture
- Software design and implementation
- Integration and integration testing
- Software qualification testing
- Configuration management
- Change management
- Quality assurance
The important distinction is that ASPICE is primarily concerned with how engineering processes are performed and managed. It does not replace functional safety or cybersecurity standards.
What does ASPICE mean for suppliers?
Consider a supplier developing an electronic control unit for an automotive OEM.
The supplier may have experienced developers and a functioning software product. However, the OEM may also expect evidence that requirements are reviewed, design decisions are documented, tests are planned, changes are controlled, and verification results are recorded.
If these activities happen inconsistently across teams, the supplier may struggle to demonstrate process capability.
An ASPICE level assessment can help identify process gaps and prioritize improvements before a formal customer assessment.
If your engineering team needs to understand its current process maturity and prepare for customer expectations, explore MicroGenesis ALM Services for support with engineering lifecycle processes and tool-enabled governance.
ISO 26262: Managing Functional Safety
ISO 26262 addresses functional safety for electrical and electronic systems in road vehicles. Its purpose is to help prevent unreasonable risk caused by malfunctioning behavior in safety-related systems.
The standard uses a lifecycle-based approach that includes hazard analysis, safety requirements, system design, hardware and software development, verification, validation, and confirmation measures.
A central concept is the Automotive Safety Integrity Level, or ASIL. ASIL classification is determined through hazard analysis and risk assessment, considering factors such as severity, exposure, and controllability.
What does ISO 26262 look like in practice?
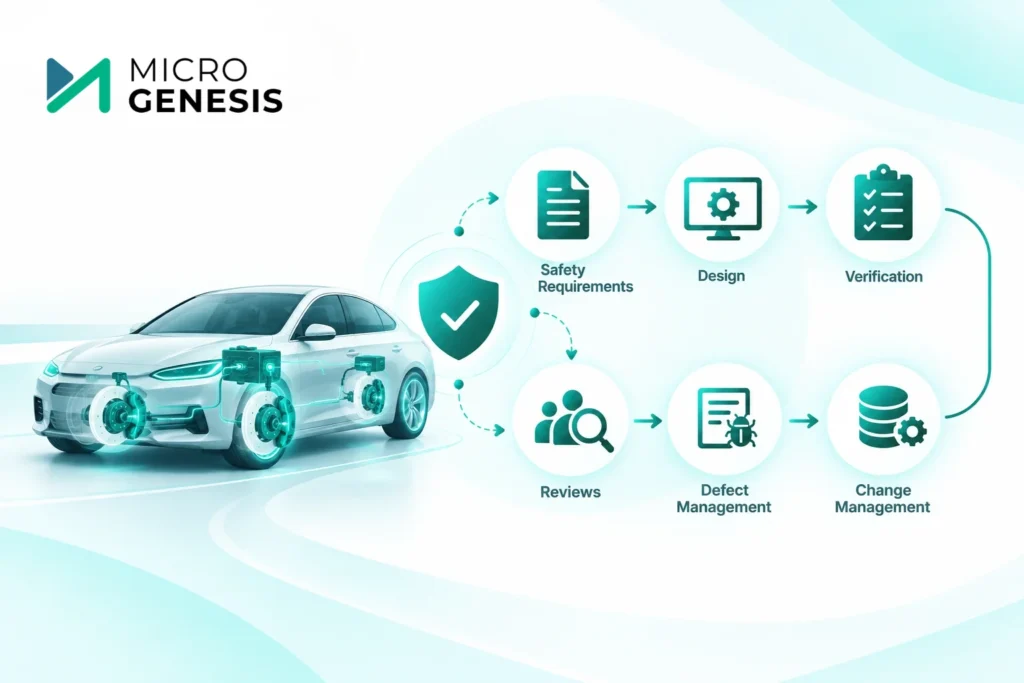
Imagine a braking control system in which software calculates the pressure required to achieve a requested braking response.
A software defect could affect vehicle behavior. The development team therefore needs to understand the relevant safety requirements, implement appropriate controls, verify the software, and retain evidence supporting the safety case.
That evidence may include:
- Safety requirements and their allocation
- Software architecture and design records
- Verification plans and results
- Reviews and analysis
- Defect records
- Configuration and change history
A safety-related requirement should not disappear into a development backlog without a clear path to implementation and verification.
For a deeper explanation, see What Is Functional Safety?. It is also useful to understand the differences between ASPICE and ISO 26262, because process capability and functional safety address related but distinct objectives.
Why testing and traceability matter
Safety-related testing must be planned around requirements, risks, and the applicable verification strategy. Test results need to be linked to the items they verify, with failures and unresolved issues managed appropriately.
Read more about test lifecycle management for regulated software and automotive software testing best practices.
ISO/SAE 21434: Automotive Cybersecurity Engineering
Functional safety focuses on risks associated with malfunctioning behavior. Automotive cybersecurity addresses threats that may arise from malicious activity, vulnerabilities, and attacks against vehicle systems.
ISO/SAE 21434 provides a cybersecurity engineering framework for road vehicles. It covers cybersecurity activities across the product lifecycle, from concept and development through production, operation, maintenance, and decommissioning, as applicable.
Typical activities include:
- Threat analysis and risk assessment
- Cybersecurity goals and requirements
- Security architecture and design
- Secure implementation
- Verification and validation
- Vulnerability management
- Cybersecurity monitoring and incident response
A practical example
Consider a connected vehicle gateway that communicates with external services and internal vehicle networks.
An assessment may identify the risk that unauthorized access could allow an attacker to send malicious messages or compromise connected functions.
The engineering team must translate the risk analysis into suitable cybersecurity requirements, design controls, verify their effectiveness, and maintain evidence of the decisions and activities.
Cybersecurity cannot be treated as a final penetration test before release. It must influence requirements, architecture, implementation, integration, and ongoing vulnerability management.
This is especially important as connected vehicles and software-defined vehicle architectures expand. The software lifecycle must support security-related changes long after the initial release.
How ASPICE, ISO 26262, and ISO/SAE 21434 Work Together
These frameworks have different purposes, but many engineering activities overlap.
Framework | Primary focus | Typical engineering question |
ASPICE | Process capability | Are development processes performed and managed effectively? |
ISO 26262 | Functional safety | Are risks from malfunctioning E/E systems addressed appropriately? |
ISO/SAE 21434 | Cybersecurity | Are cybersecurity risks managed throughout the vehicle lifecycle? |
Consider a requirement for a vehicle control function.
- ASPICE helps establish disciplined requirements, development, verification, and configuration processes.
- ISO 26262 provides the functional safety framework where the function is safety-related.
- ISO/SAE 21434 addresses cybersecurity risks where the function or its interfaces are exposed to relevant threats.
A supplier may need to satisfy multiple expectations using related engineering activities and evidence. However, satisfying one framework does not automatically establish compliance with the others.
The practical goal is to avoid unnecessary duplication while preserving the specific analyses, controls, and evidence required by each framework.
How OEMs Enforce Compliance on Suppliers
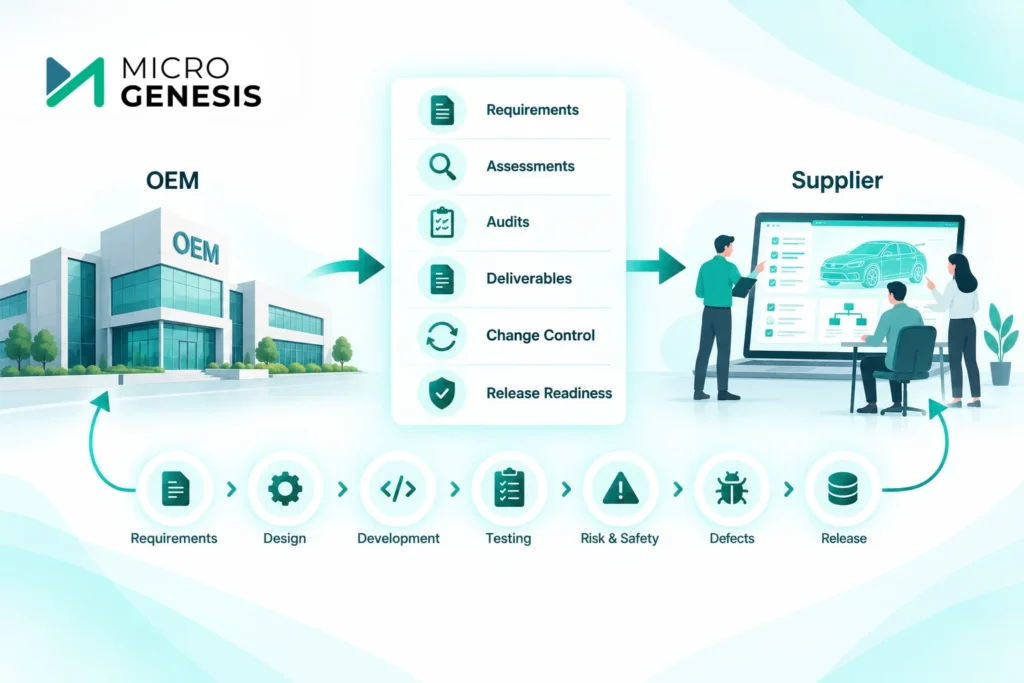
OEMs typically communicate compliance expectations through supplier requirements, contracts, quality agreements, project-specific deliverables, audits, assessments, and technical reviews.
The exact process varies by OEM, project, product, and applicable requirements.
Supplier selection and capability assessment
OEMs may evaluate a supplier’s engineering processes, quality systems, technical expertise, previous assessment results, and ability to provide required evidence.
A supplier’s engineering capability can influence sourcing decisions and project responsibilities.
Process assessments and audits
OEMs may conduct or commission ASPICE assessments, functional safety reviews, cybersecurity assessments, and project audits.
Suppliers may be asked to demonstrate that defined processes are implemented consistently and supported by appropriate work products.
Engineering deliverables and reviews
Throughout development, suppliers may need to provide requirements, architecture documents, risk analyses, verification plans, test results, configuration records, and other agreed deliverables.
The required evidence depends on the project and applicable framework.
Change control and traceability
Suppose the OEM changes a system requirement after software development has started.
The supplier may need to identify affected requirements, architecture elements, software components, tests, safety or cybersecurity analyses, and release baselines.
Without reliable traceability, even a small change can trigger extensive manual investigation.
Release readiness
Before a milestone or release, OEMs may review open defects, verification status, unresolved risks, configuration baselines, and required approvals.
A product that appears technically complete may still face delays if the required evidence is missing or inconsistent.
Suppliers preparing for an OEM assessment can benefit from reviewing their functional safety compliance tools and workflows and identifying where engineering evidence is difficult to maintain.
Where Software Lifecycle Management Fits In
Software lifecycle management provides the structure for managing engineering information and activities from requirements through development, testing, release, and maintenance.
This is where Application Lifecycle Management (ALM) becomes particularly useful.
An ALM environment can help teams connect:
- Requirements and approvals
- Architecture and design records
- Risk and safety-related information
- Cybersecurity requirements
- Development changes
- Test cases and results
- Defects and corrective actions
- Configuration baselines
- Release evidence
The value is not simply storing these records in one place. It is maintaining meaningful relationships between them and controlling changes as the product evolves.
Example: A requirement changes late in development
Suppose an OEM modifies a requirement affecting a safety-related software function.
Without connected lifecycle management, the supplier may need to contact multiple teams, update spreadsheets, check test records manually, and determine which documents need revision.
With well-configured lifecycle workflows, the team can use established traceability relationships to identify affected items, assign updates, record verification results, and maintain the relevant change history.
The tool does not make engineering decisions or guarantee compliance. The organization must still apply the appropriate engineering processes, competent reviews, and required approvals.
However, lifecycle management can make those processes more consistent and the supporting evidence easier to maintain.
For more information, explore requirements management for automotive software development and engineering traceability.
Building a Compliance-Ready Software Lifecycle
A practical starting point is to review how requirements, safety, cybersecurity, development, and verification activities currently work together.
Organizations can begin with the following steps:
Map applicable requirements. Identify relevant standards, OEM-specific expectations, contractual commitments, and project deliverables.
Assess current processes. Review how requirements, risks, development, testing, and change management are performed.
Identify traceability gaps. Check whether requirements connect to relevant design elements, implementation records, tests, and results.
Review the toolchain. Identify disconnected systems, duplicated information, manual handoffs, and weak reporting.
Standardize workflows. Define ownership, reviews, approvals, baselines, and change control.
Integrate tools where valuable. Connect requirements, testing, development, and release activities according to engineering needs.
Monitor and improve. Track process findings, open issues, verification status, and recurring gaps.
For teams implementing these practices, integrating test management with requirements tools can help address a common source of traceability gaps.
CTA: If your organization needs to improve lifecycle traceability, standardize engineering workflows, or connect disconnected development tools, explore IBM Engineering Lifecycle Management services and Codebeamer ALM services.
Why Businesses Choose MicroGenesis
Automotive software compliance requires more than understanding standards. Organizations need practical ways to apply engineering processes, maintain traceability, manage changes, and produce reliable evidence throughout development.
MicroGenesis supports engineering organizations with ALM consulting, implementation, configuration, and integration services that help connect requirements, development, testing, and lifecycle governance.
Businesses work with MicroGenesis to:
- Improve lifecycle traceability: Connect requirements, engineering changes, and verification activities.
- Strengthen ALM processes: Configure workflows that support engineering governance and controlled change management.
- Connect engineering tools: Reduce manual handoffs and improve information flow across development and testing systems.
- Support enterprise ALM platforms: Access services for IBM Engineering Lifecycle Management and PTC Codebeamer.
- Improve visibility: Make it easier to understand requirements status, verification progress, open issues, and release readiness.
- Build a practical improvement plan: Identify workflow gaps and prioritize changes based on engineering needs.
The right approach depends on your current tools, OEM requirements, product risks, and engineering maturity. No ALM platform alone guarantees compliance, but a well-designed lifecycle environment can help teams execute processes more consistently and maintain supporting evidence.
Looking to strengthen your automotive software lifecycle? Explore MicroGenesis ALM Services to discuss your requirements, traceability, toolchain integration, and lifecycle management needs.
Final Thoughts
ASPICE, ISO 26262, and ISO/SAE 21434 address different aspects of automotive engineering, but they all reinforce the need for disciplined development, controlled changes, and reliable engineering evidence.
OEMs expect suppliers to demonstrate not only that software works, but also that the development process and relevant safety and cybersecurity activities meet applicable requirements.
The most effective way to prepare is to build compliance into everyday engineering work rather than treating it as a final documentation exercise.
By connecting requirements, risk management, development, testing, and release activities through a well-managed software lifecycle, automotive organizations can improve visibility, reduce manual evidence collection, and respond more effectively to customer assessments.
If your team is preparing for an OEM assessment or improving its compliance processes, MicroGenesis can help evaluate your ALM environment and identify practical opportunities to strengthen engineering lifecycle management.